A well-known security testing tool – you can look for vulnerabilities in your own systems before someone else does

If using OSSN:
OSSN version:
Website URL (optional):
If facing any bug:
PHP Version :
Error Log if any:
Browser:
OS (Window/Linux/Android/iOS/Mac):
:)
Analysis of the instances used in the attacks shows that attackers prefer to use Chinese models (mainly DeepSeek Flash). This is due to their balance of possibilities, low costs and lack of noticeable security in a situation where prompt is properly built.
External LLM models (OpenAI, Anthropic, DeepSeek) can be connected to ARTEX. The framework itself coordinates activities between models and requires human coordination of operations.
ARTEX significantly reduces the time needed to carry out an effective, multi-stage cyberattack. In some cases, the time from choosing a goal to gaining access to the company is 3h
The framework allows even inexperienced attackers to conduct complex operations aimed at multiple targets at the same time. (...) it radically accelerates the implementation of attacks and increases the scale of their action.
What exactly can ARTEX do? Let's start with something that cyberphilosophers have not dreamed of:
Agents showed the real possibility of carrying out an attack on the supply chain, including replacing applications with iOS (extracting developers' access data - e.g. from leaks)
Google adds in its report:
ARTEX can carry out full-scale break-in divided into phases (reconnaissance, obtaining the first execution of the code on the server (so-called bridgehead), escalation of permissions (to the admin), further exploration of the network, permanent nesting in the network, data theft)
Translated https://sekurak.pl/fbi-wydalo-ostrzezenie-o-aktywnym-uzyciu-autonomicznego-opensourceowego-systemu-ai-do-hackowania-artex/
Most of time it may give false positive results.
Will contact you soon for upgrade i still remember :)
Due to the many requests in the past for additonal features and components we have decided to develope a premium version. Features like Hashtags, Videos, Polls, Events, Stories, Link Preview, etc included in it.
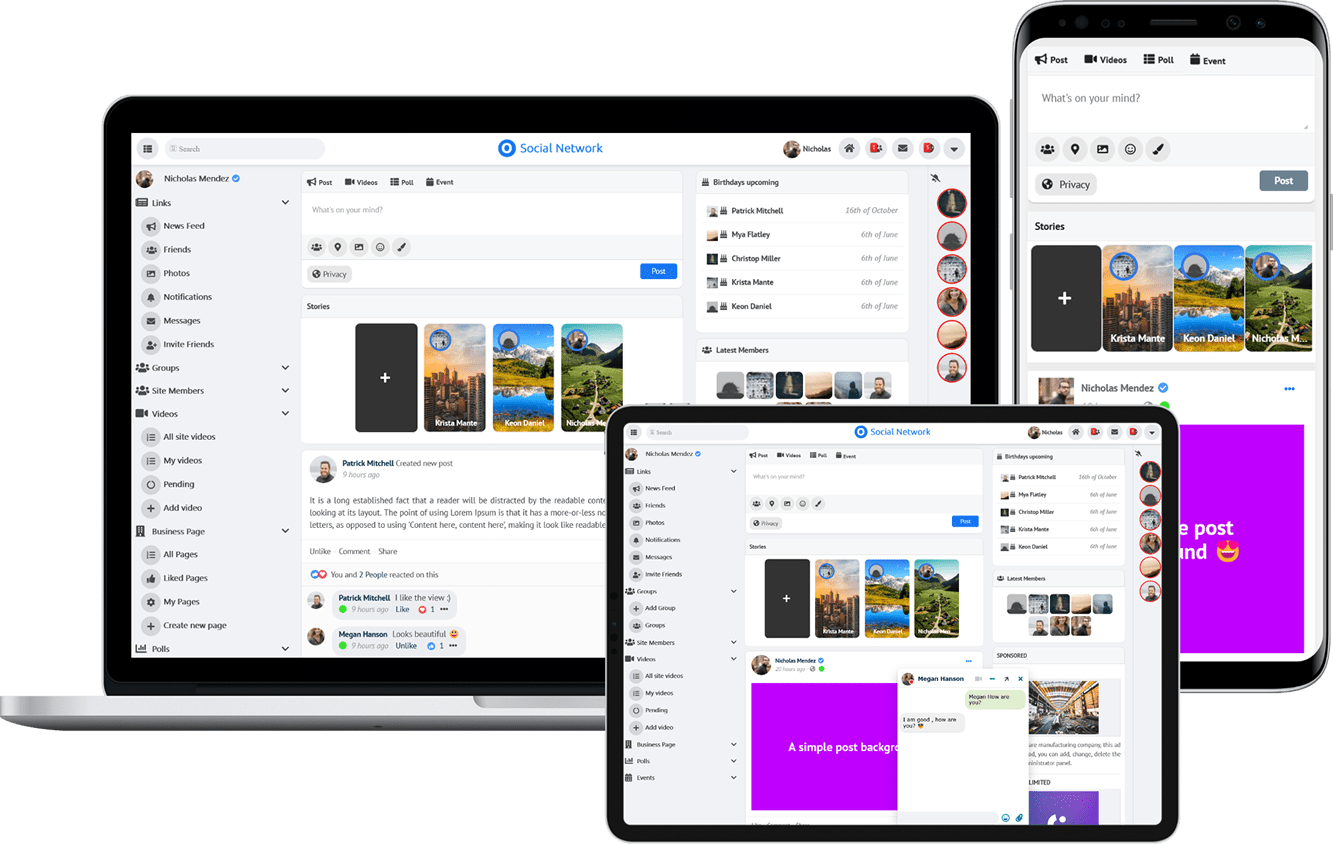 $149 (Life Time)
Learn More